Industry
Ebrol in Identity Governance
One of 10 directions Ebrol could take — a possibility explored in full, not a commitment. The buyer picks one, picks several, or holds the whole menu as optionality.
Identity governance is the working discipline that defines, audits, and enforces the access landscape of an operating organization. Its working questions are precise: who has access to what; on what basis; for how long; with what exception handling; with what audit trail. Most working enterprises answered these questions for decades through a combination of manual access reviews, ticket-based provisioning, and Excel-based access-recertification campaigns; the result was a working access landscape that drifted continuously from declared policy. The modern identity-governance category emerged in response. Working platforms in the space — typically classified as IGA, identity governance and administration — provide working machinery for role mining, policy-as-code authoring, automated provisioning and deprovisioning, separation-of-duties enforcement, and audit-evidence generation. The working market is mature in the sense that the category exists; it remains immature in the sense that most working enterprises still operate with significant working drift between declared and effective access. Ebrol enters this market with a working positioning thesis: most working IGA platforms are structured around access-as-a-list, where the working access landscape is modeled as the union of every working entitlement granted to every working user. Ebrol models the working access landscape as access-as-a-policy, where the working effective access of any working principal is the working evaluation of a working policy graph against the working principal's working attributes at the working moment of access. The distinction is consequential: access-as-a-list scales linearly with the working number of users and entitlements, and degrades as the working organization grows; access-as-a-policy scales with the working number of policy nodes, which tends to plateau even as the working organization grows. The working operating model places Ebrol underneath the working IAM platform (Okta, Azure AD, Ping Identity) and above the working downstream resource systems. Ebrol does not replace the working IdP; it instruments the working policy graph that determines who, under the working IdP, can do what. The working integration footprint covers the working dominant SaaS surface (Salesforce, Workday, ServiceNow, NetSuite, GitHub, AWS, GCP, Azure resource hierarchies) and supports working custom integrations via a working policy-evaluation API. The working buyer is the working chief information security officer, the working head of identity, or the working VP of governance, risk, and compliance. The working sales motion is working enterprise — multi-stakeholder, security-architecture-vetted, procurement-cycled. The working pricing is working seat-based with a working policy-graph upper bound.
Scenarios
Three plausible products or platforms within this vertical. Pick the angle that fits — the rest reveal once you commit. Or click "show all" if you want the static grid back.
Which spark sounds most like you?
Scenario · 01 of 3
Mid-Market IGA Platform
A working IGA deployment for mid-market enterprises (1,000-10,000 working employees) replacing a working legacy access-recertification spreadsheet workflow with a working policy-graph platform. Working integration with the working IdP and the working dominant SaaS surface.
Enterprise Policy-as-Code Migration
A working migration engagement for working large enterprises (10,000+ employees) moving from a working legacy IGA installation to Ebrol's working policy-as-code model. Working role-mining, working policy-graph authoring, working audit-evidence migration.
Compliance-Driven Audit Readiness
A working deployment focused on working audit-readiness — SOX, SOC 2, ISO 27001, PCI DSS — where the working customer's working primary working acquisition driver is working evidence-quality for working external audit cycles.
Product Concepts
Named, described, and visualized so the brand feels alive. Nothing here is a promise — use them, rename them, replace them, or leave them on the site as ambient proof that Ebrol has legs.
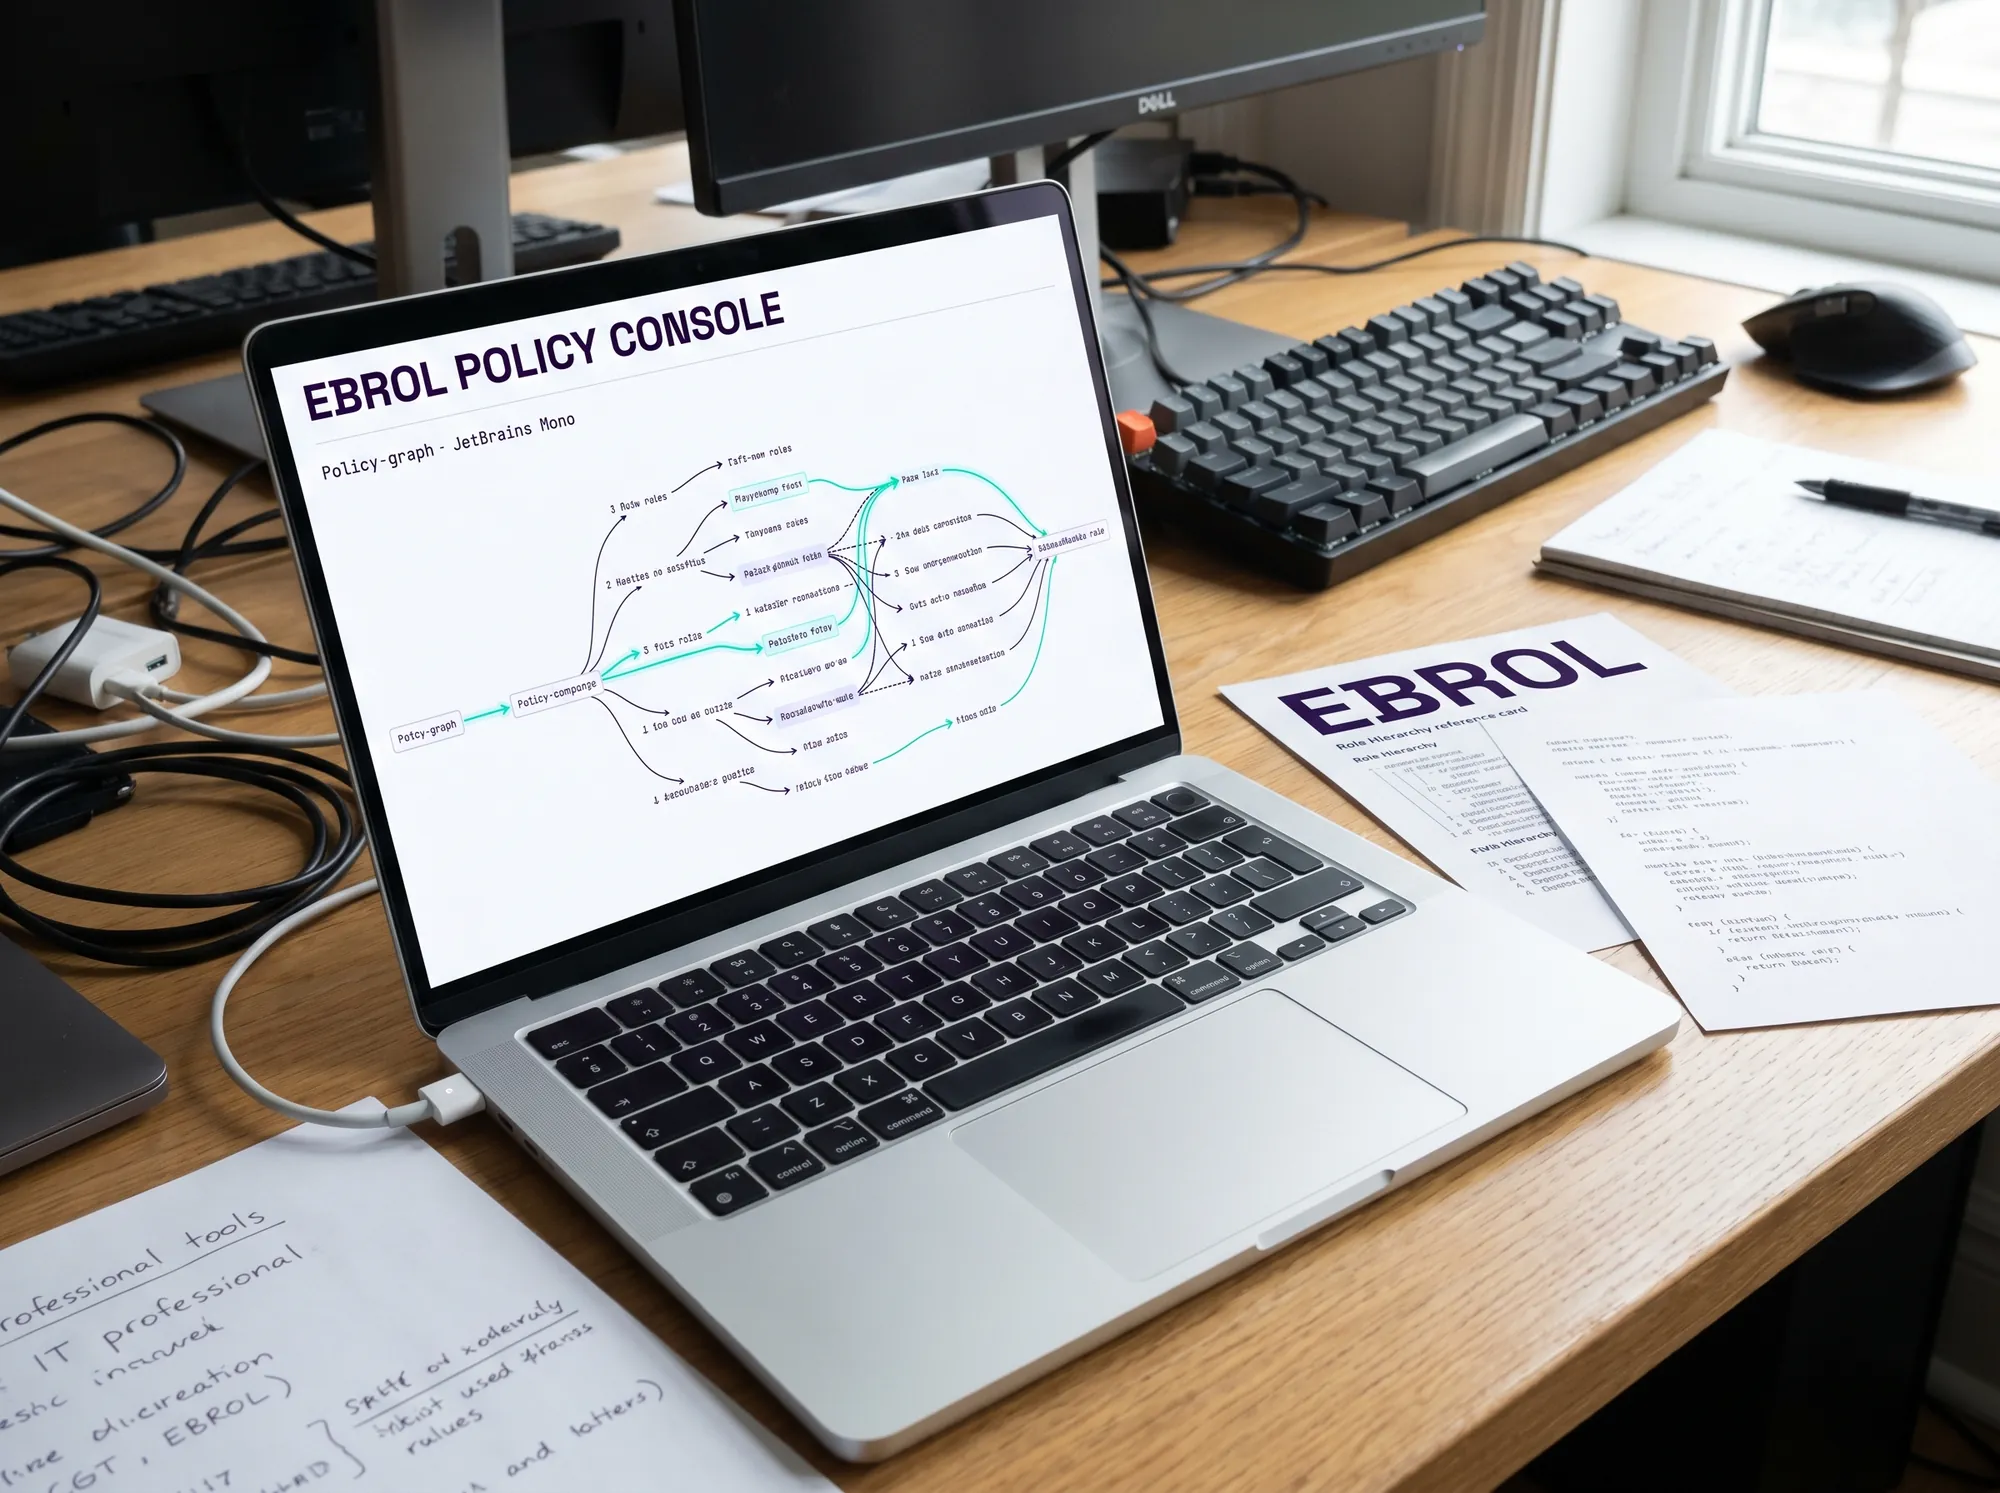
Digital
Ebrol Policy Console
The working web application for IGA administrators and architects — role hierarchy editor, policy-graph authoring, attribute predicate management, audit-evidence query interface. Single-pane working architecture; no separate workflow tool.
$48,000–$240,000 / year per enterprise
Ebrol Implementation Playbook
A perfect-bound printed implementation guide for working customer security architects — discovery, role-mining, policy-as-code rollout, audit handoff. Foil-stamped wordmark, JetBrains Mono body type.
Included with deployment
Apparel
Ebrol Field Engineer Polo
A cotton-pique polo for Ebrol field engineers and customer-success engineers in deep violet (#2A1240) with the EBROL wordmark embroidered in cool near-white (#FAFAFB) Space Grotesk bold caps above the heart, electric cyan (#00E5C5) accent stripe at the cuff.
$58
Stationery
Ebrol Implementation Notebook
A pocket-sized soft-cover notebook for field engineers and customer security architects — working integration log fields, working role-mining note fields, working policy-rollout checklist. Cool near-white cover with foil-stamped wordmark.
$26
Hardware
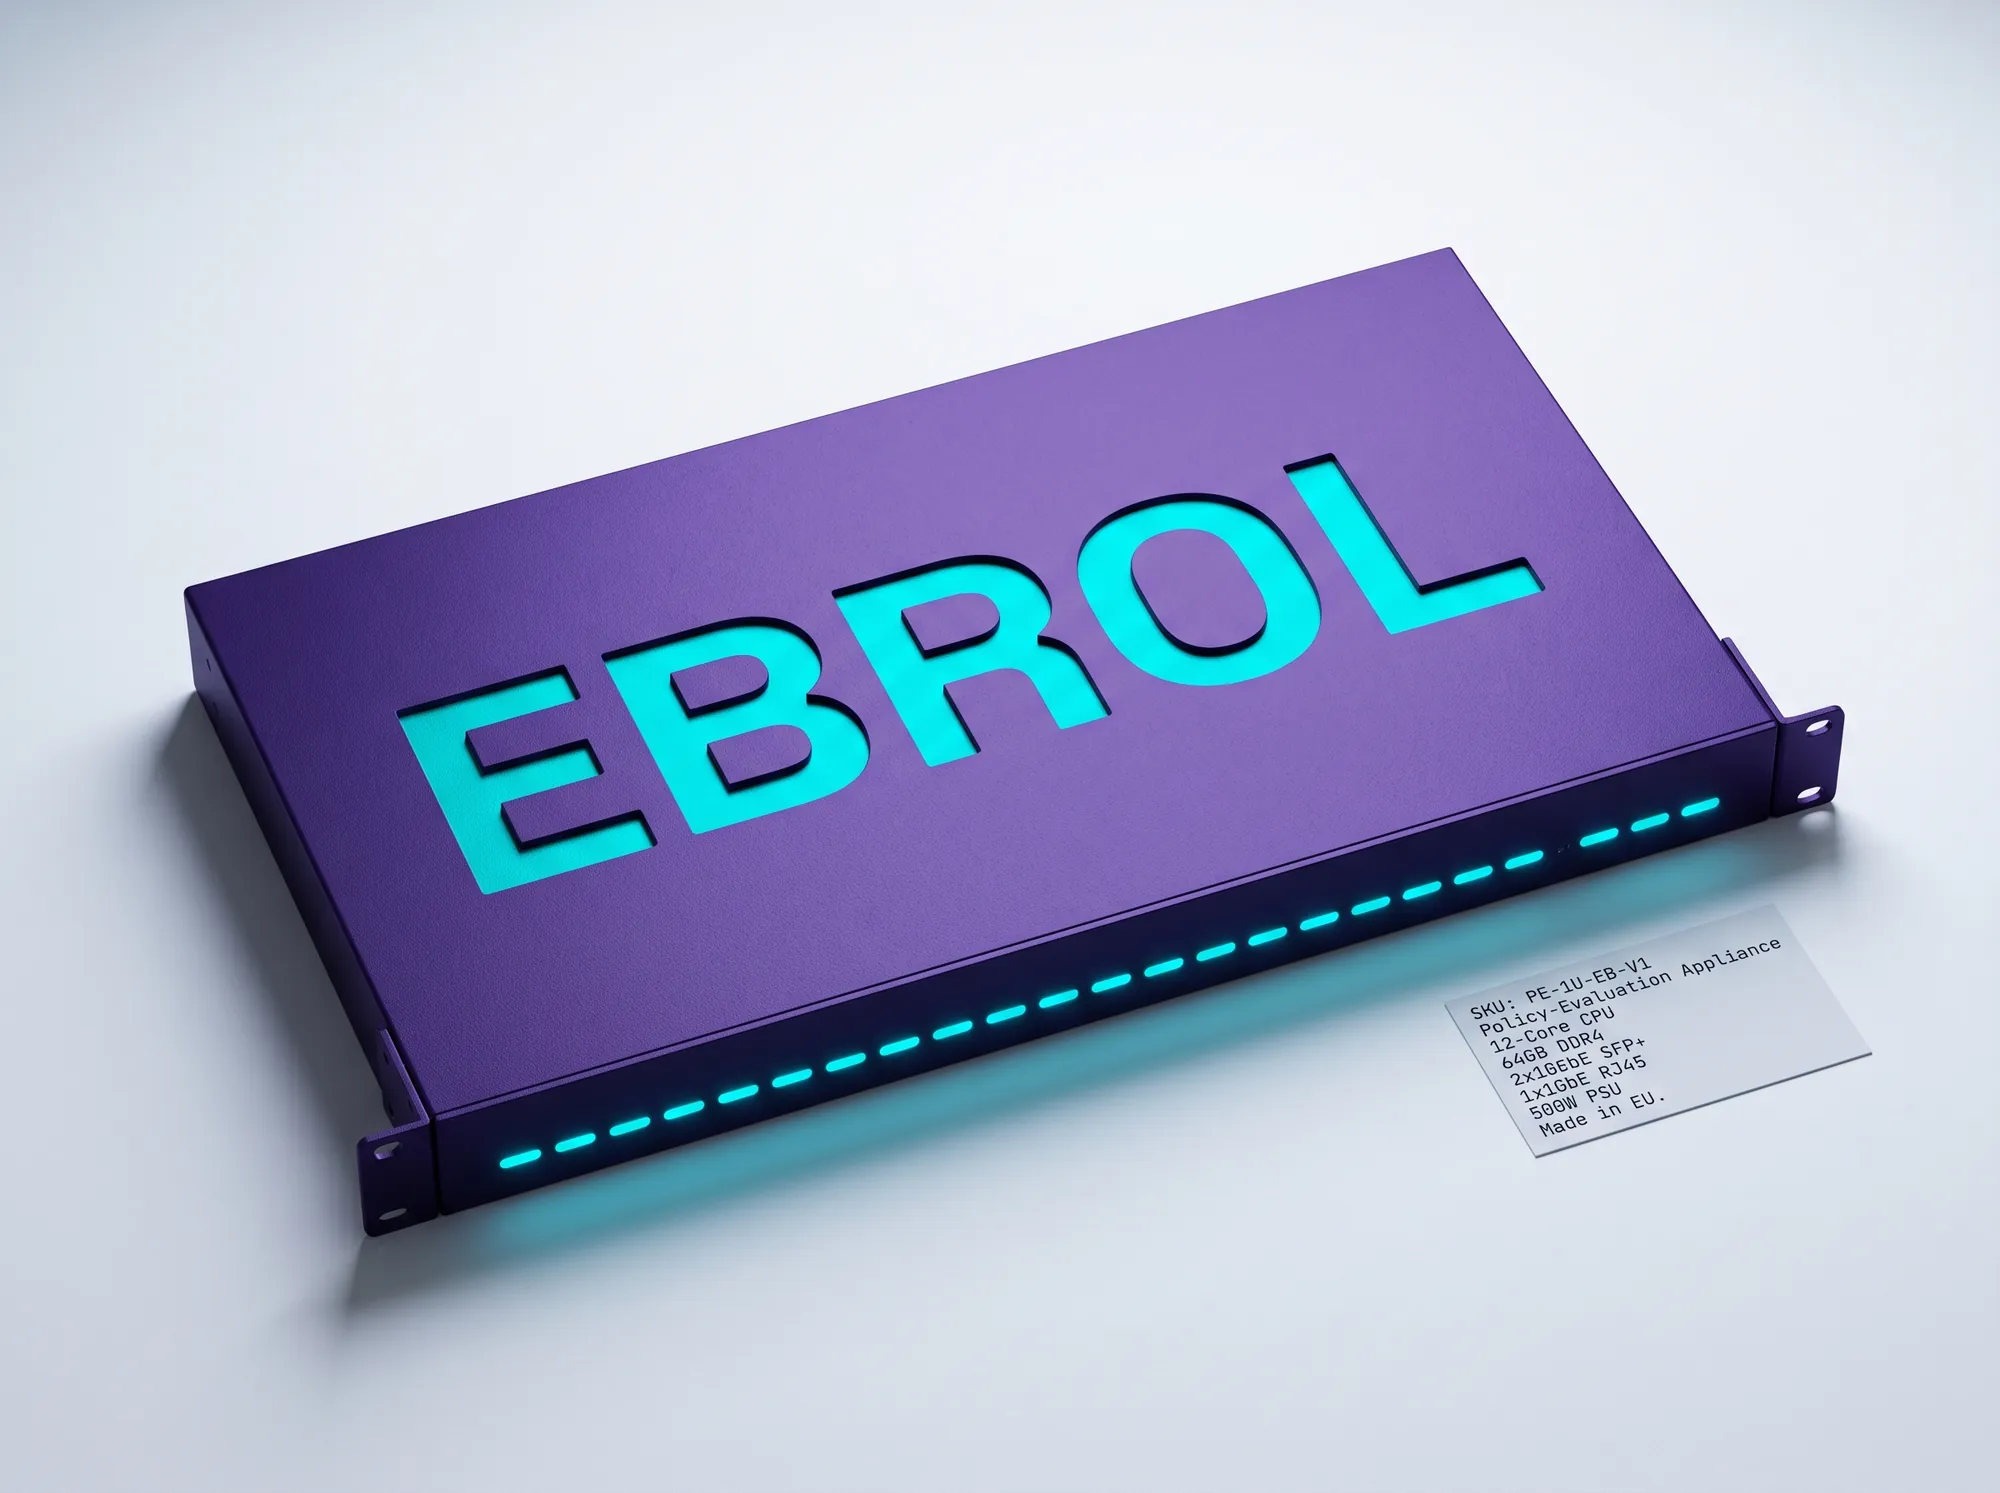
Ebrol Policy Evaluation Server
Working customer-deployable policy-evaluation server hardware — 1U rackmount appliance for working customer environments where working SaaS evaluation is not permitted. Deep violet finish, EBROL stamped on the bezel in electric cyan.
$24,000 / appliance
Environmental
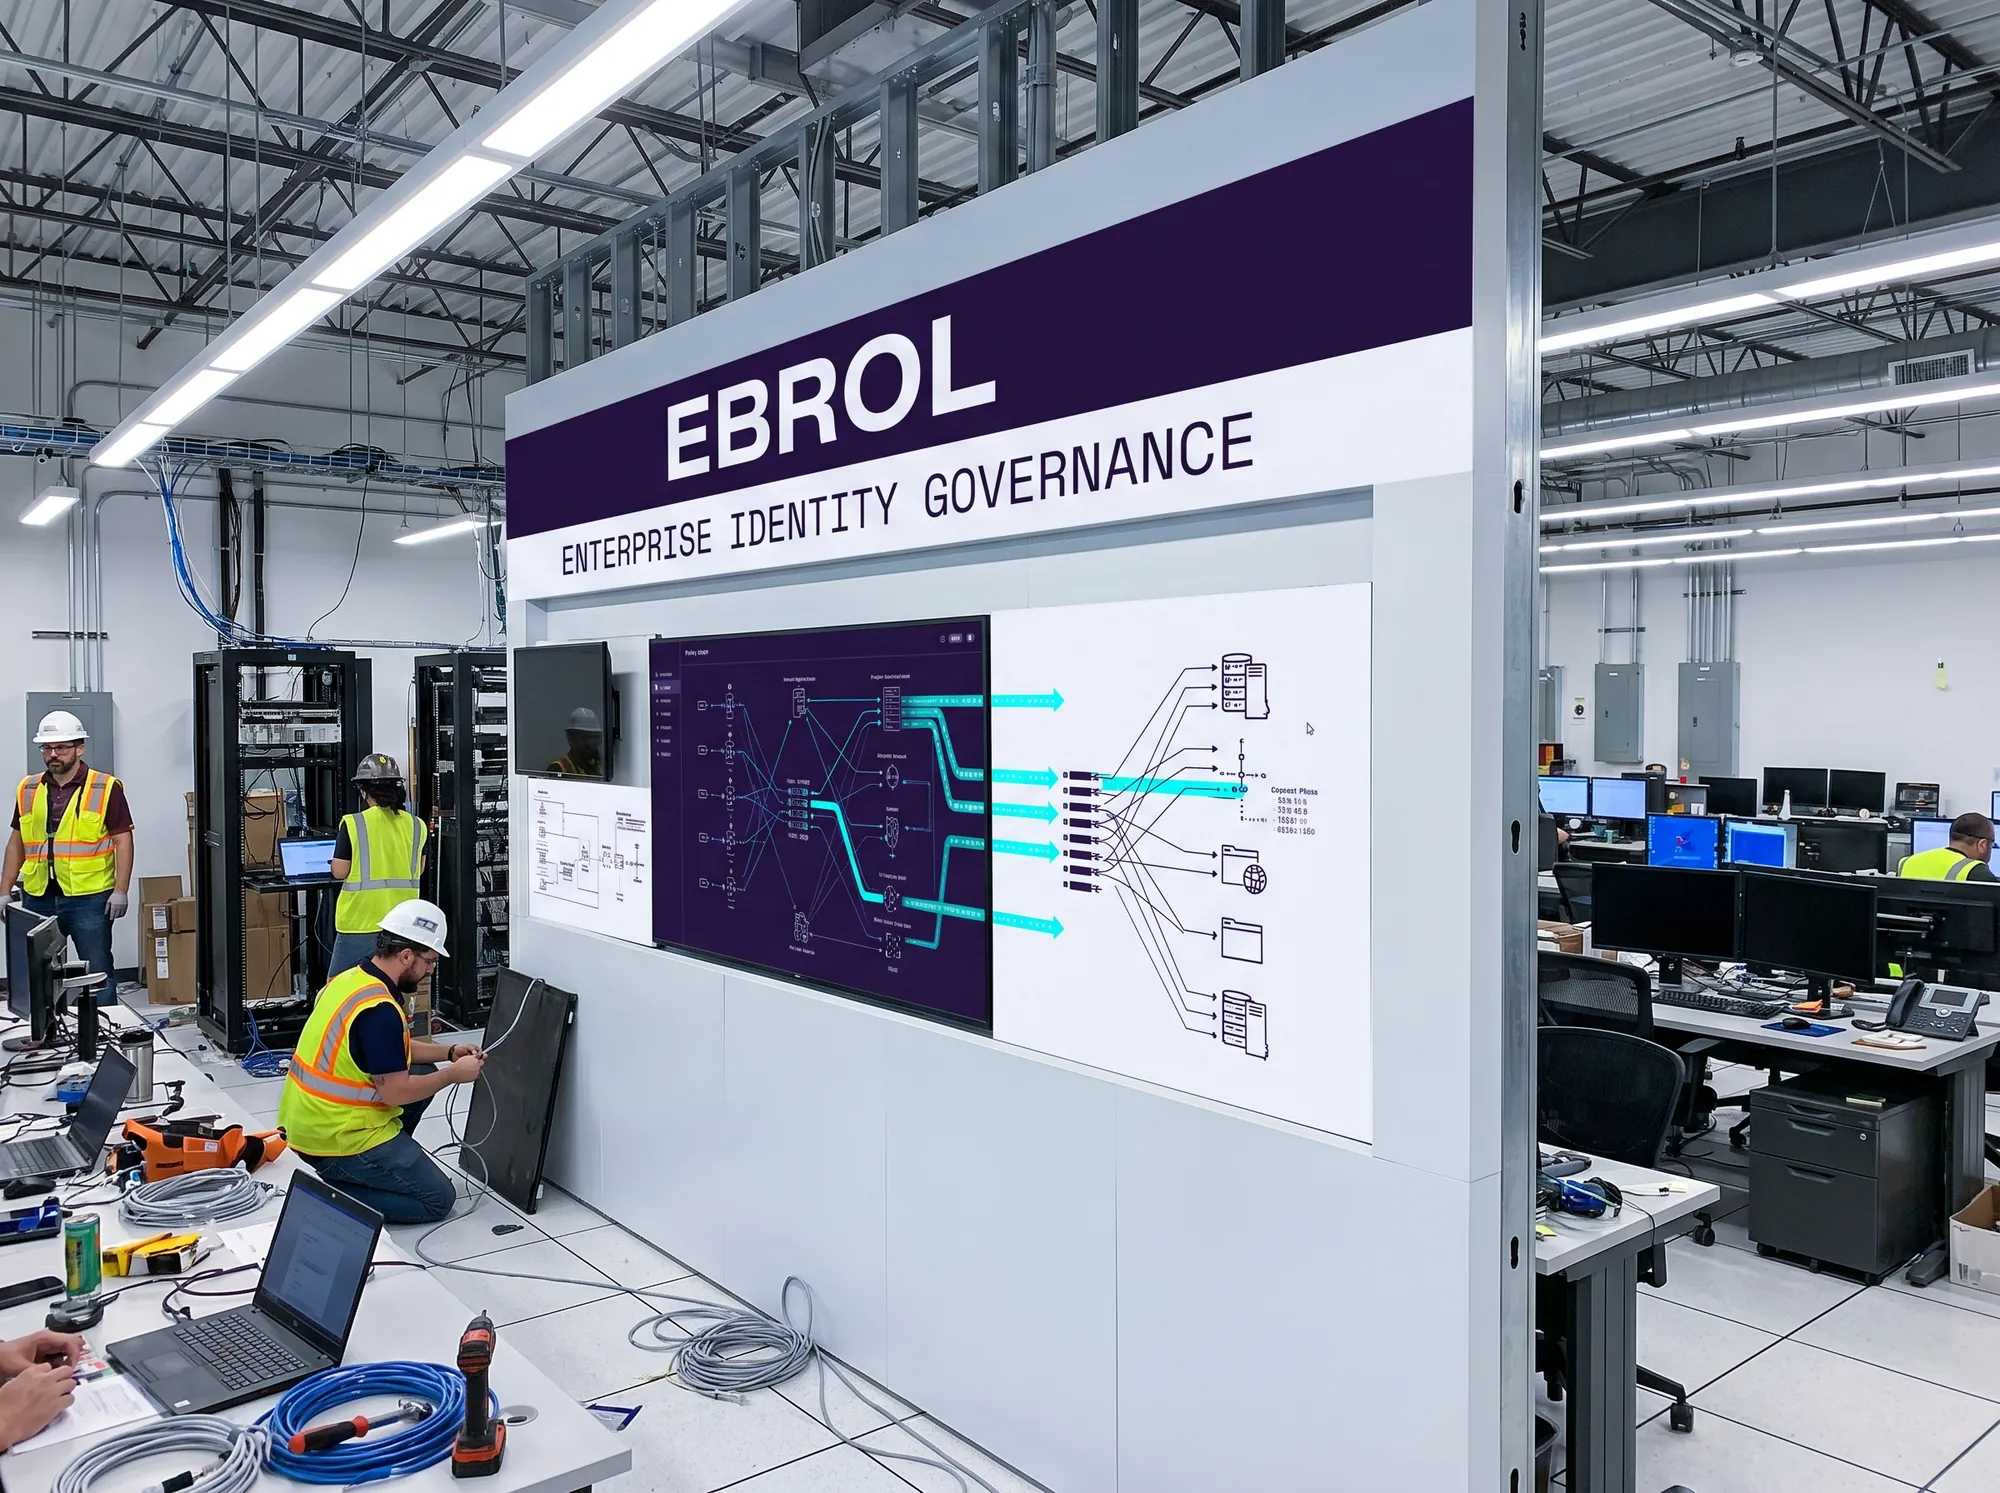
Ebrol Operations Center Build-Out
A working customer-side operations-center wall build-out for security-operations centers running Ebrol — wall-mounted policy-graph display, deep violet wordmark band, JetBrains Mono caption strip. Designed for SOC and IGA war-room contexts.
$42,000 / installed
Radio Ad Script
Thirty seconds of Ebrol in this vertical. Visitors often play it twice — and every listen makes the brand a little more familiar in their head. That familiarity belongs to the owner.
“It's the morning of the audit. The working access-recertification spreadsheet has nine open exceptions, and the working external auditor's working evidence request is in the inbox. Ebrol exports the working policy-graph trace in fourteen seconds. Roles, defined. ebrol.com.”
For the investor
Identity Governance is one of 10 directions.
Ebrol reads as the encoded role. The brand sits on the wall of an enterprise security operations center, on the spine of a SOX evidence binder, on the bezel of a customer-deployable policy-evaluation appliance, and on the architecture diagram pinned above a working IAM platform engineer's desk. The .com is yours. The working policy-graph thesis is yours. The working vertical product surfaces, the working consulting practice, and the working appliance line are yours. The asset accumulates while the buyer reviews it.